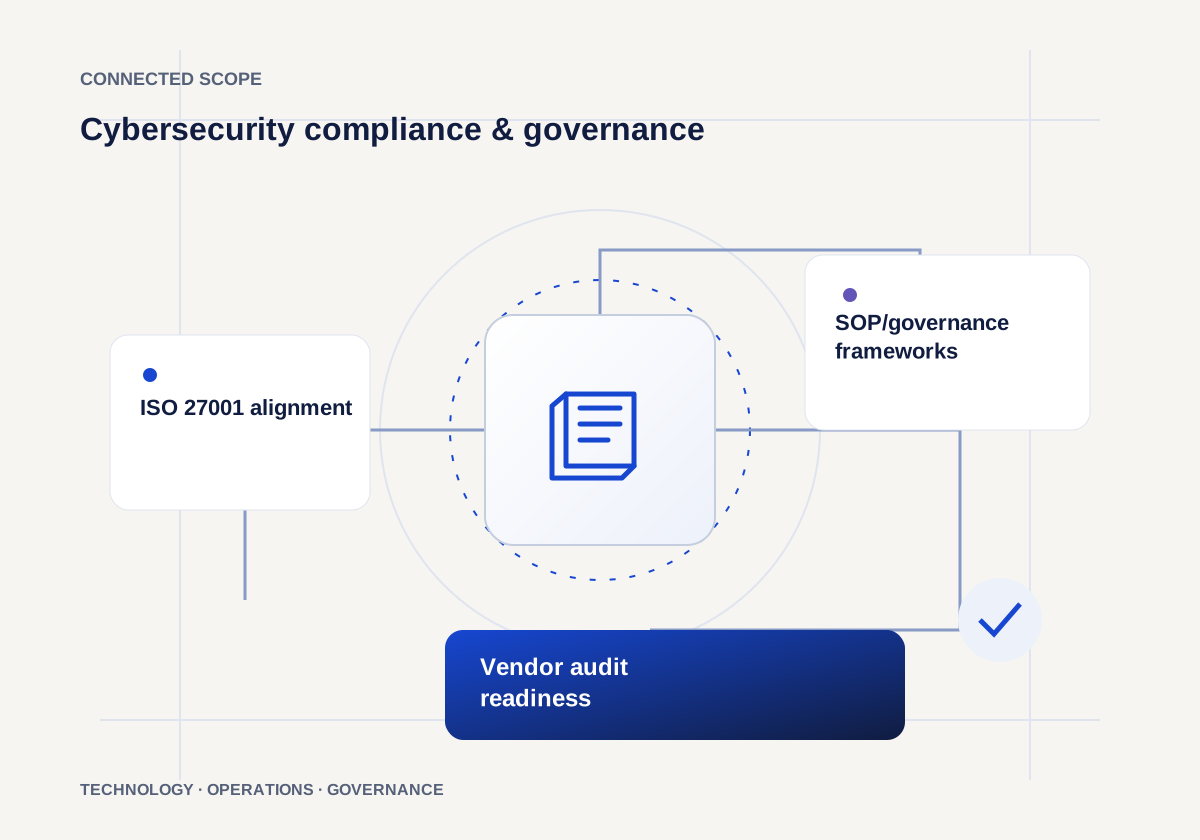
ISO 27001 alignment
Map security processes, risks and relevant control evidence to an agreed ISMS scope.
ISO 27001 alignment, SOP frameworks and vendor audit readiness.
Operating context
Make security responsibilities and operating evidence reviewable. The work connects technical controls with policies, access records, corrective actions and the requirements of an agreed customer or assessment scope.
A business-aligned solution with agreed validation evidence and an owned operating model.
Map security processes, risks and relevant control evidence to an agreed ISMS scope.
Prepare owned operating procedures, approval boundaries and review routines.
Organize customer questionnaires, technical evidence and tracked follow-up actions.
Maintain review records, finding ownership and improvement priorities.
Map the agreed customer/framework requirements to owned controls and evidence; the applicable program and assessment scope are confirmed before work.
Plan your engagement
Cybersecurity compliance support organizes security risks, operating procedures and control evidence within an agreed framework. Rektrs scopes ISO 27001 alignment, governance documentation and vendor audit readiness with accountable owners and tracked actions.
An agreed view of systems, risks, current controls and missing evidence, with prioritized actions and owners. The framework and organization scope should be defined before comparing requirements.
No. Procedures need implementation evidence, reviews and maintained responsibilities. A customer's audit or an independent assessment can require additional checks and remains outside consultancy approval authority.
Before implementation
We confirm your current systems, locations, process owners and required outputs. The proposal sets milestones, dependencies, acceptance criteria and support responsibilities for the agreed scope.