Patch management
Coordinate update policy, deployment checks and exception visibility.
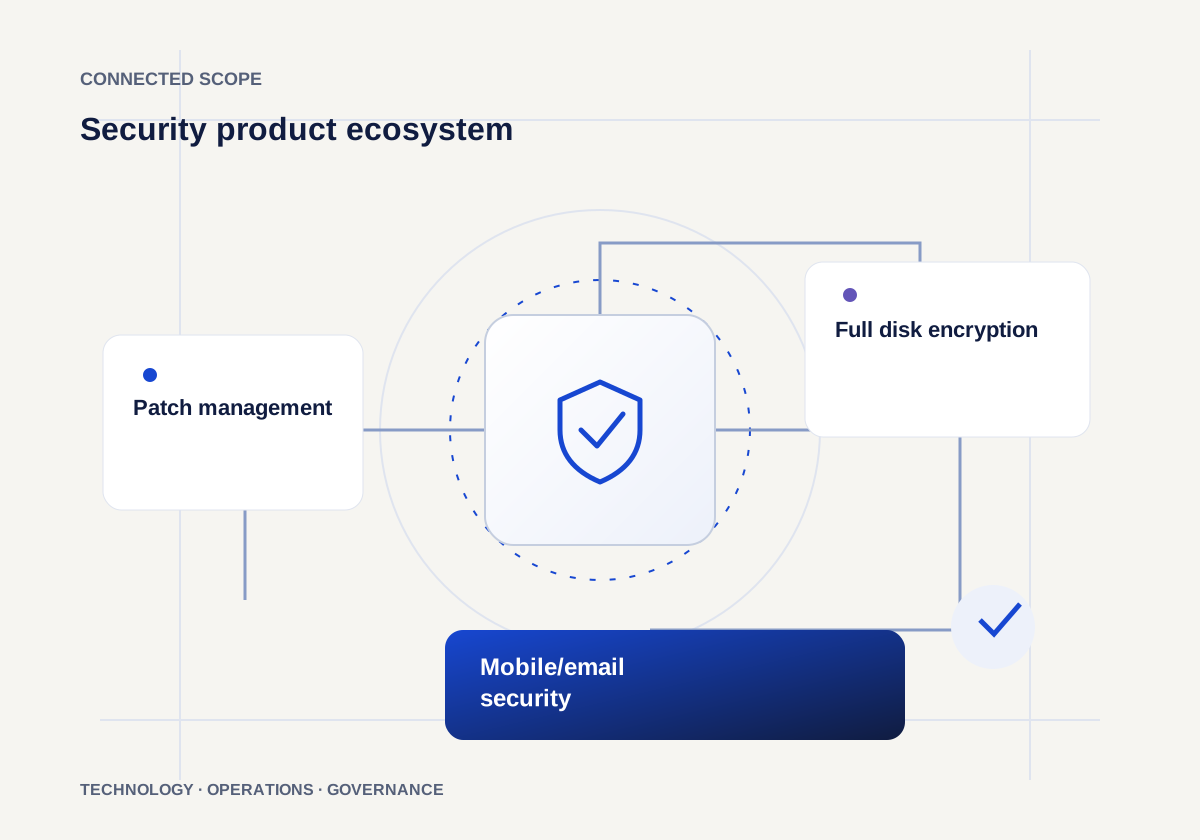
Patch, encryption, mobile/email, CSPM+, container, sandbox and ransomware controls.
Operating context
Integrate selected security products into an owned control and response model. Product selection considers the estate, licensing, deployment dependencies and the team responsible for ongoing operation.
A business-aligned solution with agreed validation evidence and an owned operating model.
Coordinate update policy, deployment checks and exception visibility.
Support device encryption policy, key custody and recovery procedures.
Connect device and mail threat controls with user access and response workflows.
Review cloud posture, workload configuration and container exposure through supported tooling.
Coordinate suspicious-content analysis with approved tools and escalation controls.
Connect prevention, privileged access, detection, backup and recovery practices.
Review unauthorized changes against agreed configuration baselines.
Coordinate client-owned smartphone and tablet policies, access and support.
Deploy or integrate selected intrusion monitoring and prevention controls.
Review encryption, access and data-loss prevention controls for scoped storage.
Support agreed Office 365 and Google Workspace protection controls.
Review unusual activity using supported detection tooling and defined response ownership.
Configure selected exploit prevention controls with validation of required business applications.
Integrate approved threat feeds and indicators of compromise (IOCs) into review workflows.
Tune supported detection models with change records, evaluation and exception review.
Before implementation
We confirm your current systems, locations, process owners and required outputs. The proposal sets milestones, dependencies, acceptance criteria and support responsibilities for the agreed scope.