Visibility
Logs, alerts, asset inventory and monitoring dashboards.
Managed detection and response with extended telemetry and contracted 24/7 coverage.
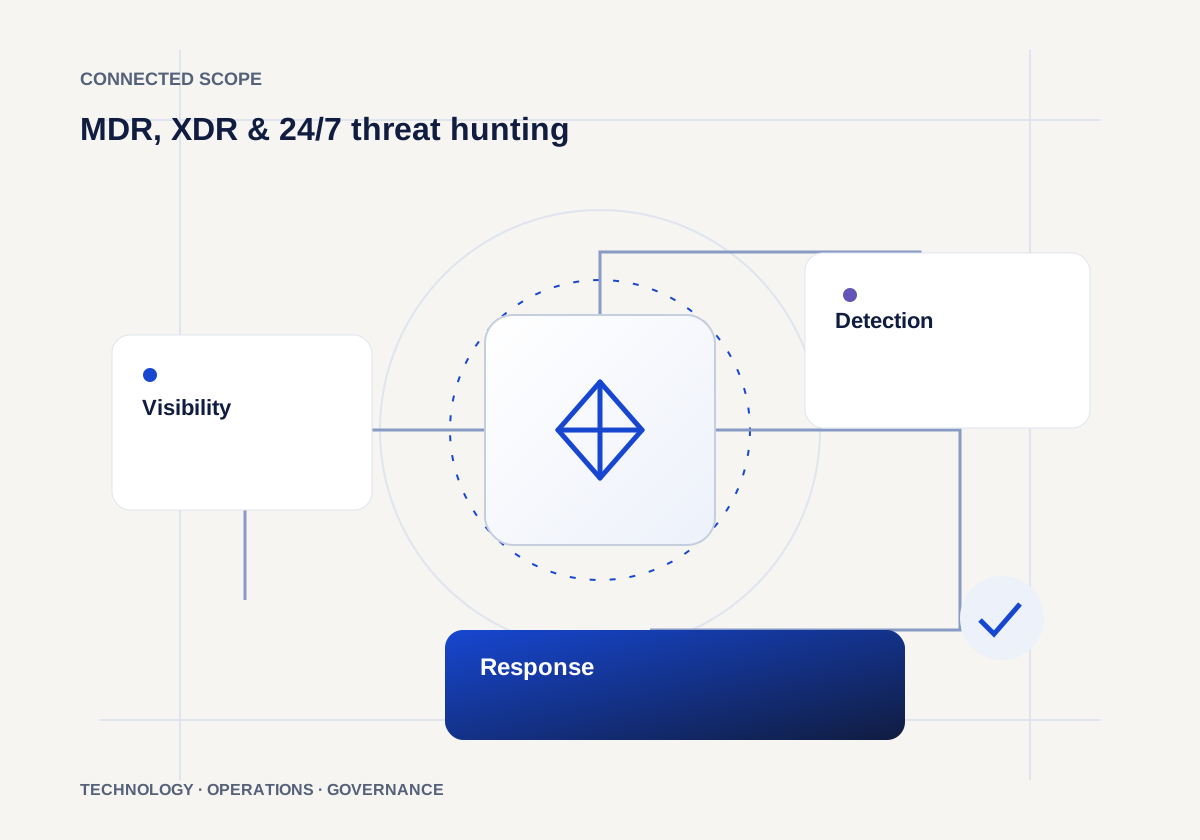
Operating context
A practical path toward stronger monitoring and incident response.
Managed detection and response focuses on finding threats quickly and responding before damage increases. Rektrs can support clients with monitoring strategy, log collection, alert workflows, incident triage processes and escalation design.
For organizations not ready for a full SOC, Rektrs can help build SOC readiness: identifying assets, logging critical systems, defining incident categories, documenting response playbooks and connecting security tools.
Coordinate security telemetry, investigation and escalation through the agreed managed-service model. Coverage, supported tools, alert categories and response authority are specified in the service agreement.
A business-aligned solution with agreed validation evidence and an owned operating model.
Logs, alerts, asset inventory and monitoring dashboards.
Rules, anomaly triggers and suspicious activity alerts.
Incident triage, escalation, containment and documentation.
Playbooks, contacts, roles and regular review cycles.
Post-incident learnings and control enhancements.
Provide contracted continuous coverage and proactive review of relevant threat signals within the agreed operating scope.
Triage alerts, investigate prioritized events and coordinate response with authorized owners.
Correlate supported identity, endpoint, network, email and cloud signals.
Maintain findings, incident records, response handoffs and improvement priorities.
Plan your engagement
Managed detection and response combines agreed security telemetry, investigation and response workflows. Rektrs defines monitored endpoints, identities, networks or cloud workloads, operating coverage, escalation contacts and authorized response actions in the service scope.
Confirm telemetry availability, asset inventory, integration permissions, severity definitions, escalation channels, evidence retention and response authorization. Coverage and SLA commitments belong in the signed scope; do not assume every system or response action is included.
Coverage follows the signed asset and integration scope. Identify available logs, endpoint agents, cloud accounts and identity sources, then confirm monitoring hours and any unsupported systems.
Agree response authority in advance, including which actions may be automated and which require your designated contact. Access restrictions and business-critical dependencies belong in the response playbook.
Define severity, contact routes, evidence retention and communication ownership. Investigation records should show what was observed, what was done and which remediation actions remain with the system owner.
Before implementation
We confirm your current systems, locations, process owners and required outputs. The proposal sets milestones, dependencies, acceptance criteria and support responsibilities for the agreed scope.
Coverage hours, response authority, retained security products and service levels are confirmed in the signed service scope.