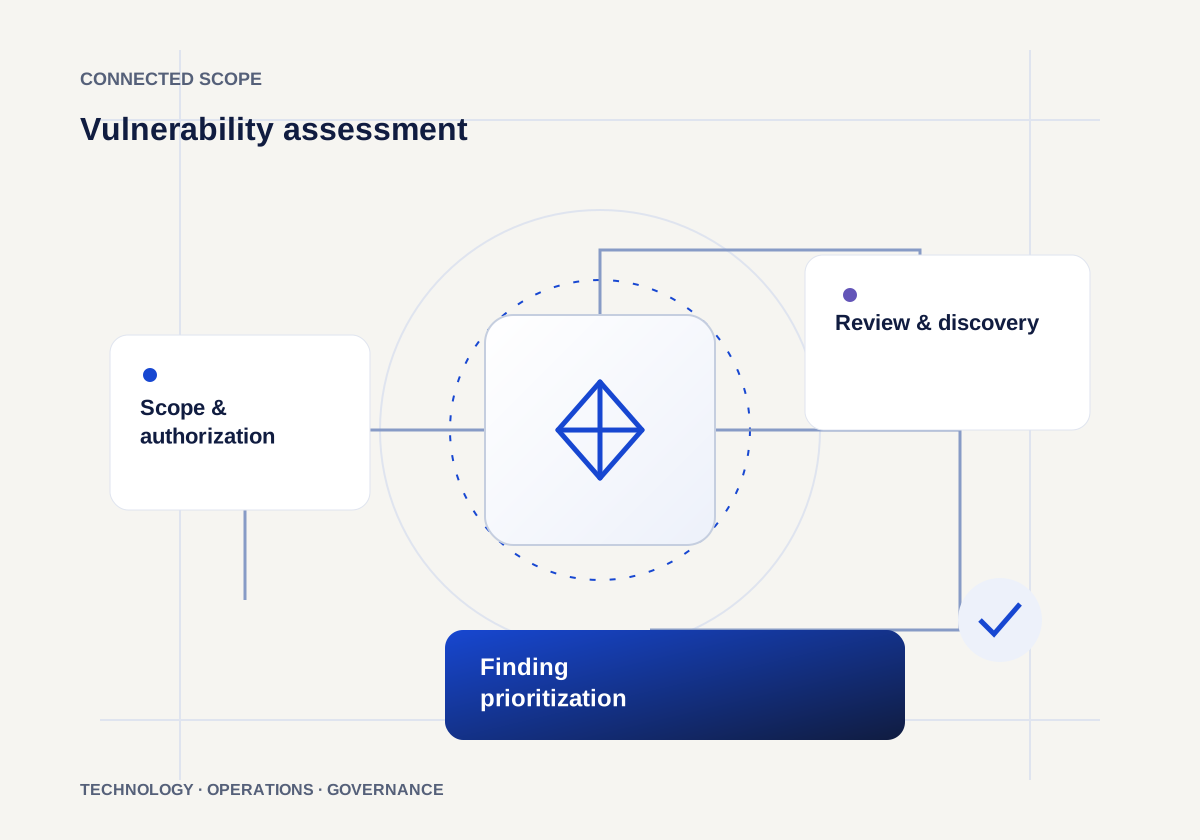
Scope & authorization
Agree assets, permitted checks, assessment windows and responsible contacts.
Identify and prioritize weaknesses across agreed applications and infrastructure.
Operating context
A scoped assessment makes technical weaknesses reviewable without presenting every finding as the same business risk.
An owned implementation, agreed review criteria and a maintainable handover.
Agree assets, permitted checks, assessment windows and responsible contacts.
Review the selected web, mobile, API or infrastructure exposure and configuration.
Explain evidence, impact and practical remediation ownership.
Agree which corrected findings require rechecking and record the outcome.
Before implementation
We confirm your current systems, locations, process owners and required outputs. The proposal sets milestones, dependencies, acceptance criteria and support responsibilities for the agreed scope.